

No WhatsApp Without Your SIM? What Every Citizen and Business Must Do Next , Guidebook
Decode India’s New Digital Safety Rules in One Handy Playbook
Guide to India’s New Sanchar Saathi & SIM‑Binding Mandates (DoT, Nov–Dec 2025)
Main takeaway: In the last few days, the Department of Telecommunications (DoT) has taken two big steps:
- Mandating pre‑installation of the Sanchar Saathi app on all phones sold in India
- Mandating SIM‑binding for messaging/OTT apps like WhatsApp, Telegram, Signal, Snapchat, etc.
Officially, this is about curbing cyber‑fraud, misuse of telecom resources, and improving traceability. Practically, it will reshape how Indians use messaging apps, how businesses run WhatsApp‑centric workflows, and how identity is tied to mobile devices.
Below is a structured, business‑oriented guide: what has changed, who is impacted, the stated vs likely unstated motives, and a stepwise playbook for businesses to realign behavior and operations.
1. What exactly has DoT mandated?
1.1 Sanchar Saathi app: compulsory, pre‑installed on all handsets
On 28 November 2025, DoT issued directions under the Telecom Cyber Security framework requiring that all mobile handsets manufactured in or imported into India must have the Sanchar Saathi app pre‑installed.
Key points from the official directions and news reports:
- Scope: All handsets meant for use in India, whether manufactured domestically or imported.
- Pre‑installation & visibility: App must be pre‑installed ,
- Visibly accessible at first use or device setup,
- Its core functionalities may not be disabled or restricted .
- Existing stock: For devices already manufactured and present in sales channels, manufacturers/importers are asked to push the app via software updates where feasible .
- Timelines: Implementation within 90 days
- Compliance report within 120 days
What Sanchar Saathi does (portal launched 2023, app launched January 2025):
- Verify the genuineness of a mobile handset via IMEI (helps detect tampered/duplicate IMEIs and stolen devices).
- Report lost or stolen phones and block them to prevent misuse.
- View and manage all mobile connections issued in your name , so you can spot unauthorized SIMs.
- Report suspected fraud communications (calls/SMS/WhatsApp) via the Chakshu feature.
- Access trusted contact details of banks/financial institutions , reducing phishing risk.
DoT frames this as a tool to curb misuse of telecom resources for cyber‑frauds and ensure telecom cybersecurity.
1.2 SIM‑binding mandate for messaging / OTT apps
On or around 28–29 November 2025, DoT issued directions under the Telecommunication (Telecom Cyber Security) Rules 2024 / Telecom Cybersecurity Amendment Rules 2025, targeting app‑based communication services that use mobile numbers (WhatsApp, Telegram, Signal, Snapchat, ShareChat, JioChat, Josh, Arattai, etc.).
Core requirements:
- Continuous SIM‑binding: Apps must remain continuously linked to the SIM card used to register the account .
- The app must stop working if that SIM is removed, replaced or deactivated in the device.
- Web/desktop sessions: Web/desktop versions (e.g., WhatsApp Web) must auto‑logout periodically , at least once every 6 hours ,
- Re‑login only through QR‑based re‑authentication tied to an active SIM.
- Timelines: 90 days to implement (so effectively by late Feb 2026),
- 120 days to submit a compliance report to DoT.
- Legal basis & enforcement: Apps that use mobile numbers for identification are classified as Telecommunication Identifier User Entities (TIUEs) , bringing them formally under telecom‑style regulation.
- Non‑compliance can attract action under the Telecommunications Act 2023 and the Telecom Cyber Security Rules .
DoT’s rationale:
- Some messaging apps continue to work even if the SIM is removed after initial verification, enabling their misuse from outside India for cyber‑fraud and other offences.
- Continuous SIM‑binding and limited‑duration web sessions are meant to plug this loophole and improve traceability and accountability .
2. Stakeholders impacted and compliance burden
2.1 Key stakeholders
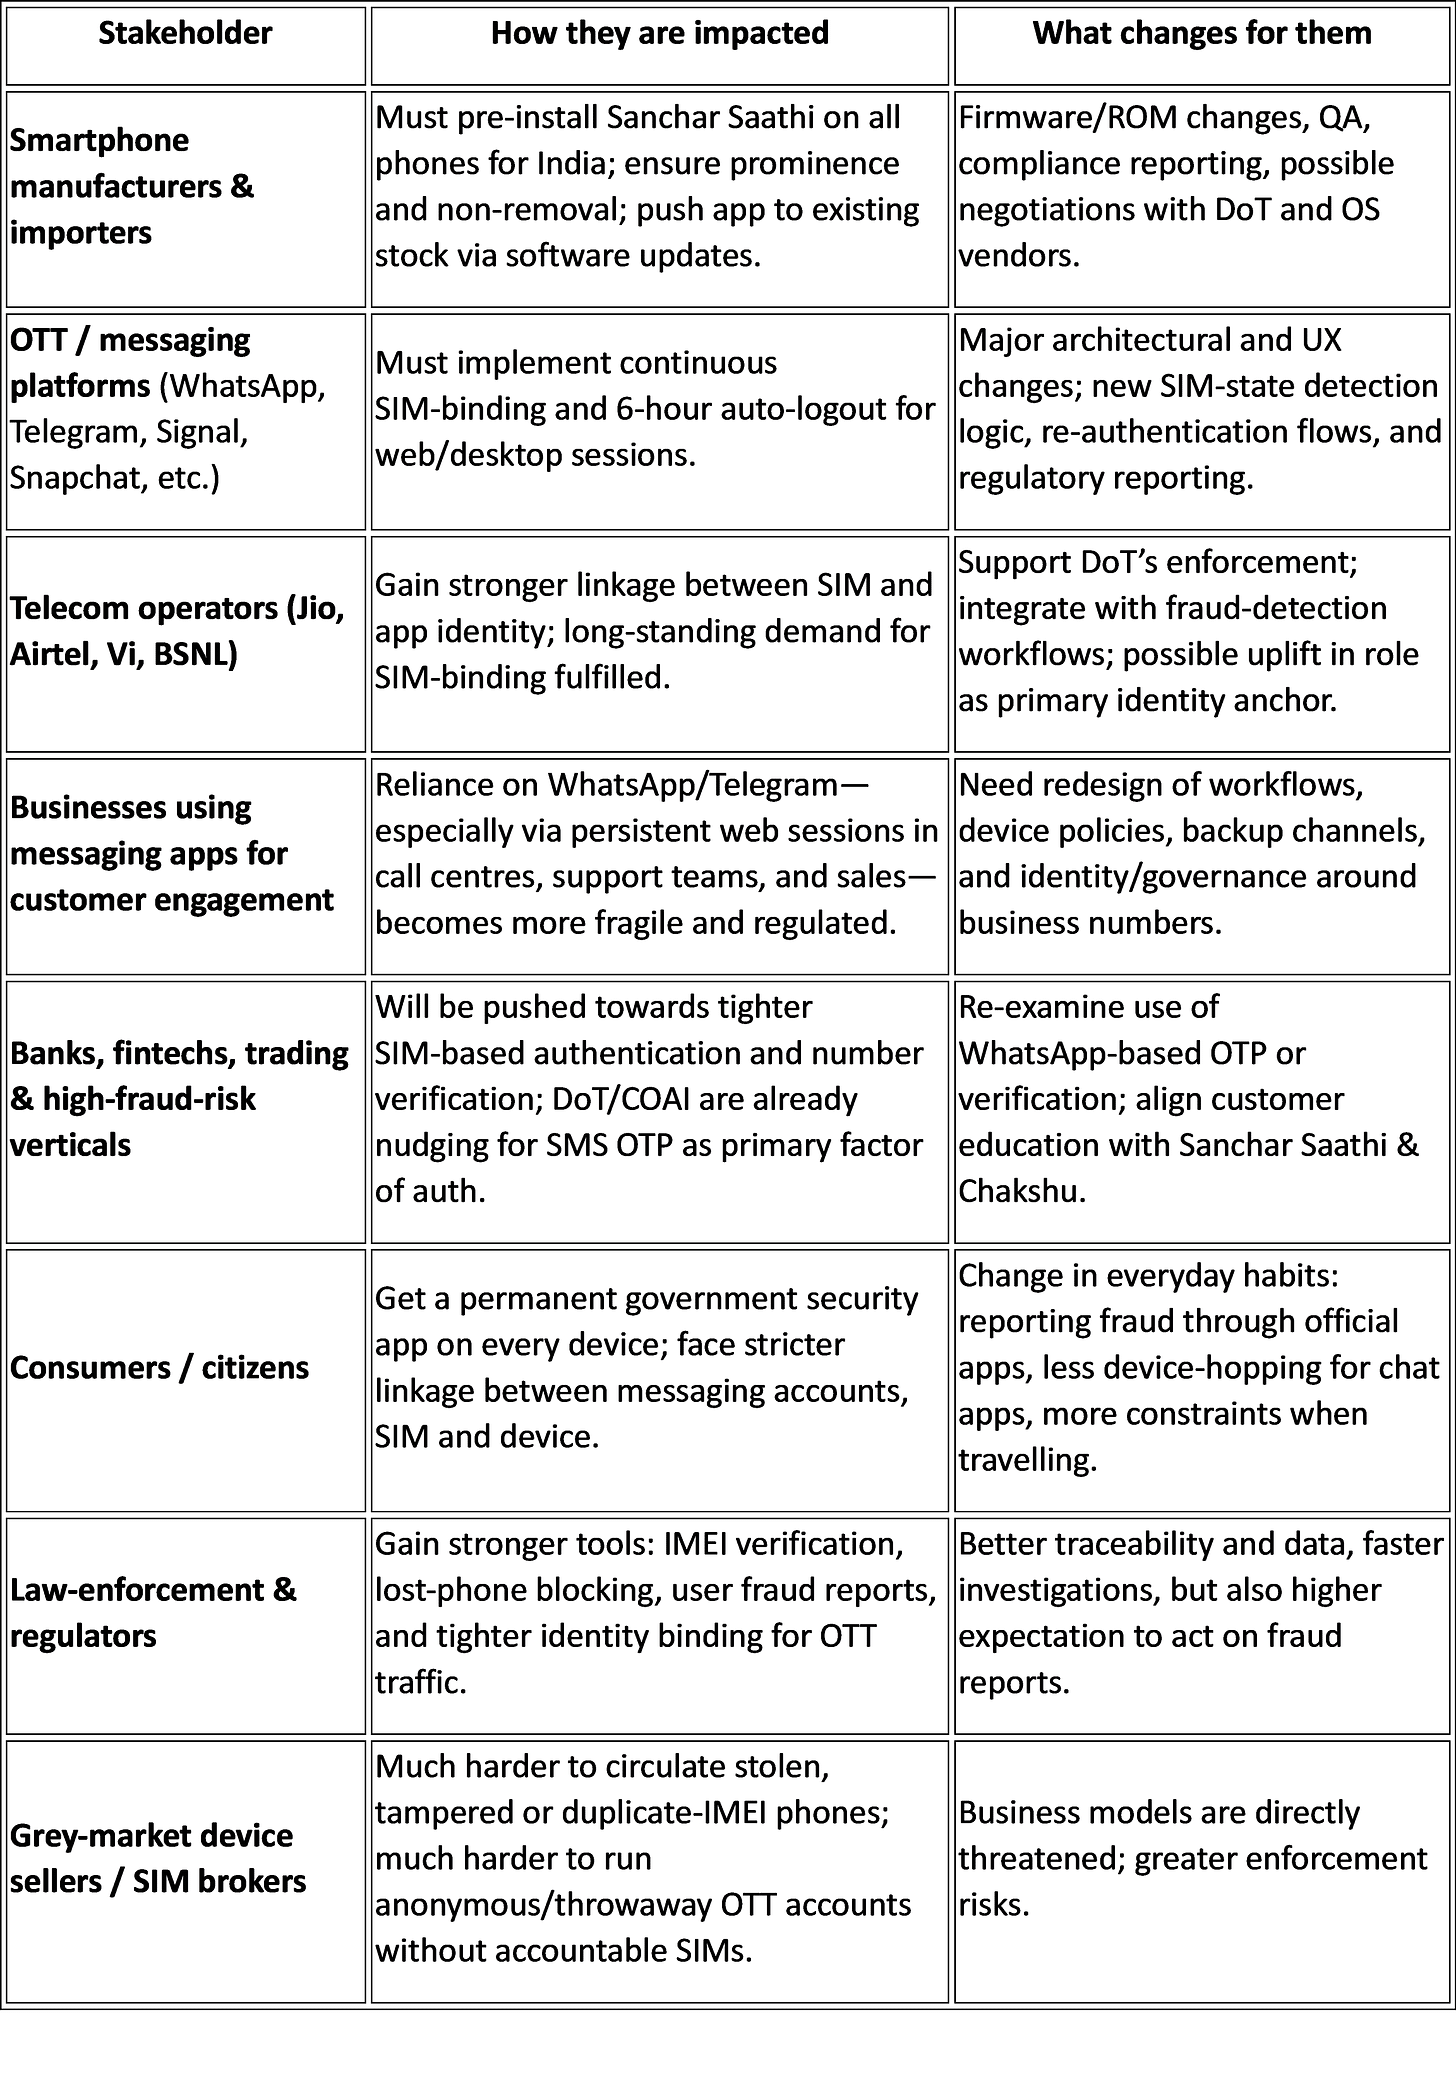
3. Official motives vs likely unstated motives
3.1 Officially stated motives
Across the PIB press release, DoT’s directions, and media reporting, the key stated goals are:
- Curb cyber‑frauds and financial scams conducted via calls, SMS and OTT apps.
- Prevent misuse of telecom identifiers (mobile numbers), SIMs, and tampered devices (duplicate/forged IMEIs).
- Improve telecom cybersecurity and national security , especially for cross‑border cyber‑crime using Indian numbers.
- Protect citizens from: buying non‑genuine or blacklisted devices,
- having SIMs issued in their name without consent,
- falling victim to spoofed calls/SMS and fraud communications.
- Enhance accountability and traceability in messaging apps by linking them more tightly to verified SIMs.
These are consistent with broader campaigns: TRAI disconnecting and blacklisting millions of fraud numbers and urging citizens to use official apps like DND and Sanchar Saathi to report spam.
3.2 Likely unstated / implicit motives (inferred)
Here the line between fact and interpretation matters. The following are not explicitly stated by the government, but are strongly suggested by policy design, past lobbying, and independent commentary:
- Expanding regulatory control from telecom to OTT/digital communication By creating the TIUE category and bringing number‑using OTT apps under telecom‑style rules, DoT significantly extends its jurisdiction beyond licensed telcos to digital platforms .
- Industry bodies like IAMAI have raised concerns about regulatory overreach and telecom‑like compliance costs for digital businesses.
- Strengthening state visibility and traceability of communication networks SIM‑binding + non‑removable government app + tighter IMEI controls together reduce anonymity and increase the ability to tie devices, numbers and app accounts to real identities , which is valuable for security agencies.
- Commentators have flagged this as a move that could enhance surveillance capabilities , even if the official framing is “cybersecurity”.
- Favouring telecom operators’ long‑standing agenda vis‑à‑vis OTT apps The Cellular Operators Association of India (COAI) has explicitly welcomed SIM‑binding as a ‘landmark’ move , closing loopholes that created anonymity and misuse through OTT apps.
- Telcos have for years argued that OTT communication providers enjoy “light” regulation while riding on telco infrastructure; this move partially levels regulatory obligations .
- Preparing ground for broader mobile‑number‑centric identity infrastructure The same policy direction mentions or aligns with a Mobile Number Validation (MNV) platform and stricter linkage between numbers and users.
- In practice, this can evolve into a more centralised number‑based identity layer , useful not just for fraud control but for future e‑governance, payments and platform regulation.
- Normalising non‑removable government apps Several commentators note that Sanchar Saathi is effectively the first permanent, non‑removable government app mandated on all smartphones , raising a wider normative issue about state software on private devices.
- This may set a precedent for future “security” or “governance” apps being bundled at OS/firmware level.
These points are strongly supported by how stakeholders and analysts are reacting—privacy debate, concerns about state overreach, and industry pushback—rather than by government statements alone.
4. How everyday behavior will change
4.1 For individuals
- Sanchar Saathi is always there: Every new phone will ship with a visible, non‑removable government security app, and many existing phones will receive it via updates.
Likely behavioural effects:
- More people will verify second‑hand phones before purchase (IMEI check).
- More direct reporting of fraud calls/SMS via Chakshu.
- More citizens discovering extra SIMs issued in their name , and getting them disconnected.
- Messaging apps tied tightly to SIM and device: No more running WhatsApp/Telegram on a phone that doesn’t have the original SIM (e.g., using Wi‑Fi only on an old phone).
- Frequent travellers who swap to foreign SIMs will face friction: they may lose access to accounts unless they keep the Indian SIM (physical or eSIM) active.
- WhatsApp Web / desktop will log out at least every 6 hours; users must re‑scan QR each time.
Net effect: more device–identity coupling, less casual or anonymous use, and more friction for power users who rely on web clients.
4.2 For businesses
Major impact areas for businesses:
- Contact‑centre and support workflows that rely heavily on 24×7 WhatsApp Web tabs.
- Sales and relationship teams that use personal phones or shared devices with multiple accounts.
- SMBs and D2C brands for whom WhatsApp/Telegram are primary channels for order taking, customer support, and verification.
- Remote and distributed teams that depend on long‑lived web sessions in browsers.
These workflows will now see:
- Forced periodic logouts , requiring process discipline to re‑authenticate.
- Hard dependency on a specific SIM being in the device hosting the core account.
- More pressure to formalise who owns which number, which SIM and which device .
5. Stepwise playbook for businesses: What to do now
Below is a practical, behaviour‑focused guide, especially relevant for Indian businesses and cross‑border operators.
Step 1: Map your dependence on OTT messaging and web sessions
Create a simple internal audit:
- Which functions use WhatsApp/Telegram/Signal (sales, support, collections, RM desks, field teams, dealers)?
- Which of them depend on web/desktop clients that are kept logged in for long periods?
- Which accounts are tied to personal numbers vs company‑owned numbers ?
You want a clear map of:
- Critical processes that are fragile under 6‑hour logouts .
- Any use of Wi‑Fi‑only devices (tablets, old phones) without SIMs.
- Any account sharing (multiple people using the same WhatsApp number).
This baseline will tell you where SIM‑binding will hurt the most.
Step 2: Fix identity, SIM and device ownership policies
In the new environment, messaging identity = SIM identity = device identity to a much greater extent.
Actions:
- Company‑owned numbers for business use: Move key WhatsApp/Telegram business accounts to company‑owned SIMs (not personal staff numbers).
- Register those SIMs with clear KYC in the organisation’s name where possible.
- Dedicated devices for core accounts: For high‑volume accounts (e.g., official brand WhatsApp, collections helpline), assign dedicated phones where the SIM always stays inserted.
- Minimise SIM swapping and device hopping.
- Policy on personal vs official use: Codify that customer comms should run on official numbers/devices , not personal staff numbers, to avoid disruption if an employee changes jobs, travels, or swaps SIMs.
This aligns internal behaviour with the emerging regulatory assumption that telecom identifiers are tightly bound to accountable entities.
Step 3: Redesign workflows away from fragile WhatsApp Web habits
Since web/desktop sessions must now log out at least every 6 hours, design processes accordingly.
Recommendations:
- Shift from “always‑on tab” to “session‑based” work: Treat WhatsApp Web like a shift tool : at the start of each shift, agents log in via QR; at the end, they log out.
- Use team SOPs so that the first task at shift start is re‑authentication.
- Consider more formal business tools: Where scale justifies it, explore WhatsApp Business Platform/API via official providers, integrated into CRM or ticketing tools.
- This can reduce reliance on a single device for day‑to‑day operations, although initial SIM and number linkage still exists. (The regulatory treatment of pure API‑based flows is not yet fully clear; keep watching for clarifications.)
- Multi‑channel strategy: Avoid over‑reliance on one messaging app. Strengthen email, in‑app chat, SMS, IVR, and web portals as parallel channels.
- Use messaging apps as front‑door engagement , but shift critical flows (KYC, payments, document uploads) into controlled web/app environments .
Step 4: Build a travel and remote‑work policy around SIM‑binding
If your teams travel domestically and internationally, you need rules that respect SIM‑binding and still keep operations smooth.
- For international travel: Prefer international roaming or eSIMs so that the original Indian number remains active in the same device.
- If staff routinely switch to foreign SIMs, consider separating personal communication devices and work devices .
- For remote staff / WFH agents: Ensure assigned devices always contain the registered SIM .
- For purely browser‑based roles, standardise the re‑auth routine and ensure sufficient QR‑code access to the master device.
Step 5: Integrate Sanchar Saathi into your risk and customer‑education playbook
Sanchar Saathi can be leveraged both internally and externally.
Internal:
- Train employees to: Verify IMEIs before onboarding new corporate devices, especially second‑hand or refurbished.
- Report suspected fraud communications using Chakshu rather than just blocking at device level.
- Periodically check how many connections exist in their name , especially where staff use personal numbers in business contexts.
External (customer‑facing):
- In sectors like BFSI, fintech, brokerage, education, immigration, or F&B franchises, update communication material to: Show official numbers and domains clearly.
- Encourage customers to verify numbers and report fraud via Sanchar Saathi and the national cybercrime channel.
- Clarify that you will never ask for sensitive data over WhatsApp/SMS.
This turns a compliance challenge into a trust‑building narrative.
Step 6: Align your own authentication and KYC flows with the regulatory direction
DoT and COAI are already pushing towards SMS‑based OTP as a primary factor of authentication, given its operator‑verified traceability.
For businesses:
- Re‑evaluate any flows where you: Use WhatsApp messages as a de‑facto OTP channel , or
- Allow important actions (password resets, high‑value transactions) based on non‑operator channels alone.
- Move towards: Multi‑factor authentication where at least one factor is SIM‑verified (SMS OTP, verified number call‑backs).
- More robust KYC around mobile numbers, especially in high‑risk sectors (fintech, gaming, crypto, high‑value e‑commerce).
This is consistent with the regulatory push towards mobile‑number‑centric identity assurance.
Step 7: Develop contingency plans and escalation playbooks
With tighter controls and higher traceability comes the risk of suspensions, blocks or investigation‑triggered disruptions, especially if your numbers are inadvertently used in suspicious patterns.
Prepare for:
- What if a key business WhatsApp number is blocked or flagged? Have backup numbers , but more importantly, clear customer communication protocols and alternate channels (email, IVR, SMS).
- What if employees’ personal SIMs are implicated in fraud? Limit critical customer flows to company‑owned numbers/devices .
- Include clauses in HR policies about sharing SIMs, devices and accounts with third parties.
- What if customers are wary of Sanchar Saathi or SIM‑binding? Offer transparent FAQs explaining that: These tools help fight fraud and protect them.
- Your organisation does not gain extra surveillance powers from the app.
- Their relationship with your brand is still governed by your posted privacy policy.
6. Evaluation: Benefits, risks, and what businesses should watch
6.1 Potential benefits (if implemented well)
- Reduced cyber‑fraud and spam: Stronger identity linkage, easier reporting, and stricter device controls should, in principle, raise the cost of running large‑scale fraud operations , especially those based on SIM farms and stolen devices.
- Higher trust in mobile‑number‑based channels: If citizens see that reporting through Chakshu, TRAI DND, and Sanchar Saathi leads to real disconnections and recoveries, trust in official numbers and channels can increase .
- Better asset hygiene for organisations: The regulations effectively force better governance over SIMs, devices, and IDs , which many organisations have historically neglected.
6.2 Key risks and criticisms
- Privacy and state overreach concerns: Mandating a permanent, non‑removable government app on all smartphones has sparked a serious national privacy debate.
- Civil‑society voices and opposition figures worry about normalising state software on private devices and the potential for function creep.
- User experience & productivity friction: 6‑hour web logouts and strict SIM‑presence requirements disrupt legitimate professional workflows , from call centres to remote teams.
- Travellers, people using eSIMs or dual‑SIM set‑ups, and multi‑device power users are all adversely affected.
- Technical feasibility and OS constraints: Industry executives have flagged that continuous SIM checks are not uniformly implementable , especially on iOS where OS‑level restrictions limit SIM‑state polling.
- This can lead to uneven implementations and edge‑case failures for users.
- Risk of over‑reliance on SIM as a single point of identity: While SIM‑binding improves traceability, it can also amplify the impact of SIM swap fraud, insider abuse at telcos, or compromised KYC processes if other safeguards are weak.
6.3 What to watch over the next 6–12 months
- Detailed implementation guidelines from DoT for TIUEs and potential clarifications on how business APIs, multi‑account usage, and device fleets should be handled.
- Responses from global platforms (Meta/WhatsApp, Apple, Google, Telegram, etc.) on how they will implement SIM‑binding in their apps.
- Judicial or regulatory challenges (e.g., petitions on privacy/overreach grounds).
- Enforcement patterns : whether DoT focuses mostly on fraud hotspots or attempts broad, strict enforcement across all use cases.
- Integration of Mobile Number Validation (MNV) platforms into banking, fintech, and high‑risk verticals.
7. How to position this as a business: from compliance to strategy
For consultants, agencies and businesses, these changes open both risk and opportunity.
Strategically, businesses can:
- Reposition their customer communications as “verified, compliant and secure”, leveraging Sanchar Saathi awareness and SIM‑binding as a hygiene factor.
- Offer compliance‑ready communication stacks (WhatsApp/API + CRM + in‑app chat + SMS) as part of solutions for clients in real estate, F&B, healthcare, immigration, and fintech.
- Develop training and playbooks for client teams on: Using Sanchar Saathi and Chakshu,
- Handling 6‑hour web session rules,
- Avoiding SIM misuse and account sharing.
Handled thoughtfully, this shift can differentiate brands that take security and customer protection seriously, while unprepared competitors struggle with disrupted messaging workflows and ad‑hoc fixes.
Kirtiraj Gohil is the founder of Blue Mango Consulting Group. Which provide Business and Management Consulting services.
Disclaimer: aim of the article is to educate everyone on what to do . It no way reflects on any policy , processes of the Government or DoT. Policy /processes are subject to change and is defined by the government. Please reverify it at your end before acting on it at your descretion.